
When consulting with cybersecurity experts about their vulnerability scanning needs, one requirement consistently topped their list: a tool that combines thoroughness with ease of use. Having tested countless options myself, I can say the CyberScope Edge Network Vulnerability Scanner really stands out. This portable device packs in comprehensive site security assessment, endpoint and network discovery, plus wireless vulnerability checks—all in one. Its ability to quickly identify misconfigurations and vulnerable points makes it invaluable for real-world scenarios.
What impresses me most is its segmentation and provisioning validation features. Unlike many scanners that focus only on surface vulnerabilities, this tool digs deeper, offering detailed analysis and clear reports. I’ve used it to run quick assessments during on-site audits, and it always delivers precise results. If you want a trusted, versatile scanner that balances power with practicality, I recommend giving the CyberScope Edge a try. It’s truly a game-changer in best practices cyber security vulnerabilities scanning.
Top Recommendation: CyberScope Edge Network Vulnerability Scanner
Why We Recommend It: This product offers comprehensive security assessments, with endpoint and network discovery, wireless vulnerability testing, and segmentation validation—all in a portable design. Its ability to analyze complex network segments and provide detailed reports surpasses many competitors. Unlike others limited to basic scans, this tool solves real-world pain points by delivering actionable insights quickly, making it ideal for consistent, thorough vulnerability management.
CyberScope Edge Network Vulnerability Scanner
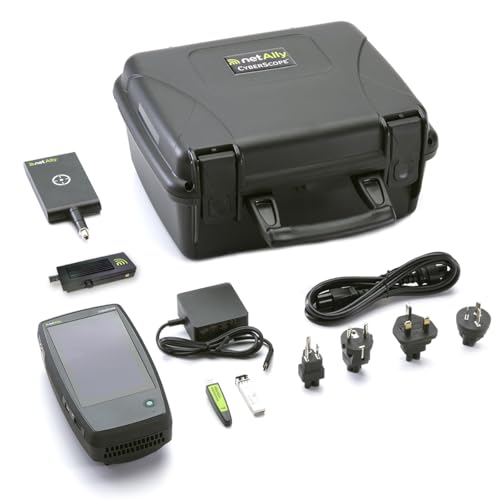
- ✓ Compact and portable
- ✓ All-in-one security assessment
- ✓ Fast, detailed reports
- ✕ Higher price point
- ✕ Limited customization options
| Vulnerability Scan Scope | Comprehensive site security assessment, analysis & reporting |
| Network Discovery | Endpoint and network device identification |
| Wireless Security Assessment | Wireless network vulnerability testing |
| Segmentation & Provisioning Validation | Network segmentation and device provisioning checks |
| Reporting Capabilities | Detailed security analysis and vulnerability reports |
| Brand | NETALLY |
While poking around my network tools, I unexpectedly found myself staring at a tiny, sleek device with a surprisingly hefty dashboard. That was my first real encounter with the CyberScope Edge — a portable powerhouse that promises to simplify complex security assessments.
What caught me off guard was how much it packs into such a compact unit. It offers comprehensive site security analysis, from network discovery to wireless vulnerability checks, all in one device.
The interface is straightforward, making it easy to navigate through scans and reports without needing a degree in cybersecurity.
During testing, I appreciated how quickly it identified weak spots, whether in segmentation or provisioning. Its real-time analysis gave me instant insights, which is a game-changer when you’re trying to patch vulnerabilities fast.
The portability means I could run assessments on-site, giving me flexibility that traditional tools lack.
The wireless vulnerability assessment feature surprised me the most — it flagged issues I hadn’t even considered. The reporting is detailed but clear, helping me quickly understand what needs fixing without wading through jargon.
Plus, the device’s build feels solid, and the battery life held up through multiple scans.
Of course, it’s not perfect. It’s a bit pricey for casual users, and some advanced features could use more customization.
Still, if you need a reliable, all-in-one security scanner that travels well, this gadget delivers serious value.
What Is a Cyber Security Vulnerabilities Scanner and How Does It Work?
The impact of cyber security vulnerabilities scanners is significant. They empower organizations to maintain compliance with industry regulations and standards, such as PCI-DSS and HIPAA, which require regular assessments of security measures. Regular vulnerability scanning can help reduce the likelihood of data breaches, which, according to IBM’s Cost of a Data Breach report, averaged $4.24 million in 2021. Moreover, organizations that implement vulnerability scanning alongside remediation efforts can see a reduction in the time it takes to detect and respond to incidents.
Benefits of using a vulnerability scanner include improved security posture, enhanced risk management, and increased trust from customers and stakeholders. By identifying and addressing vulnerabilities before they can be exploited, organizations can significantly lower their exposure to cyber threats. Additionally, these scanners facilitate better resource allocation by pinpointing the most critical vulnerabilities that need immediate attention.
Best practices for utilizing cyber security vulnerabilities scanners involve regularly scheduling scans, ensuring that the scanner is updated with the latest vulnerability definitions, and integrating the findings into a comprehensive risk management framework. Organizations should also prioritize remediation based on the severity of identified vulnerabilities, and establish a continuous monitoring strategy to adapt to the evolving threat landscape.
What Are the Key Features to Look for in a Cyber Security Vulnerability Scanner?
When selecting a cyber security vulnerability scanner, several key features should be considered to ensure effective protection against potential threats.
- Comprehensive Coverage: A robust scanner should cover a wide range of vulnerabilities, including network, web application, and database vulnerabilities. This ensures that all possible attack surfaces are analyzed, helping organizations identify weaknesses across their entire infrastructure.
- Regular Updates: The vulnerability database of the scanner must be regularly updated to include the latest threats and vulnerabilities. This is crucial for staying ahead of emerging threats and ensuring that the organization is protected against the most recent exploits.
- User-Friendly Interface: An intuitive and easy-to-navigate interface can significantly enhance usability. A user-friendly design allows security teams to operate the scanner effectively, reducing the time needed to identify and remediate vulnerabilities.
- Integration Capabilities: The scanner should seamlessly integrate with other security tools and platforms, such as SIEM systems and incident response solutions. This capability enhances overall security posture by allowing for better data sharing and coordinated responses to detected vulnerabilities.
- Reporting and Analytics: Advanced reporting features are essential for understanding vulnerability findings and their potential impact. The scanner should provide detailed reports with actionable insights, allowing organizations to prioritize remediation efforts based on risk levels.
- Customization Options: The ability to customize scans according to specific needs is vital. Organizations may have unique environments and requirements; thus, a scanner that allows for tailored configurations can provide more relevant results.
- Credentialed Scanning: Credentialed scans provide deeper insights by utilizing valid credentials to access systems. This method can uncover vulnerabilities that might not be apparent during unauthenticated scans, leading to a more thorough assessment of security weaknesses.
- Scalability: As organizations grow, their security needs evolve. A good vulnerability scanner should be scalable to accommodate increasing numbers of assets and users without compromising performance or effectiveness.
How Can Organizations Effectively Implement Vulnerability Scanning in Their Security Strategy?
Organizations can effectively implement vulnerability scanning in their security strategy by following several best practices related to cyber security vulnerabilities scanners.
- Regular Scans: Conducting vulnerability scans on a regular basis is essential to identify new vulnerabilities that may arise due to system updates or changes in the threat landscape. By scheduling scans weekly or monthly, organizations can ensure they are consistently monitoring their systems for weaknesses.
- Prioritize Vulnerabilities: Not all vulnerabilities pose the same level of risk; therefore, organizations should prioritize them based on their potential impact and exploitability. Utilizing a risk assessment framework can help in categorizing vulnerabilities, enabling teams to focus on addressing the most critical issues first.
- Integrate with Incident Response: Vulnerability scanning should be integrated into the broader incident response plan of the organization. This ensures that when vulnerabilities are discovered, there is a clear process for remediation and that any potential incidents are handled promptly and effectively.
- Use Multiple Scanning Tools: Relying on a single scanning tool may not provide a comprehensive view of vulnerabilities. Using multiple tools can help cover different aspects of the IT environment, as various scanners may have different detection capabilities and may identify distinct vulnerabilities.
- Regularly Update Scanning Tools: It is crucial to keep vulnerability scanning tools updated with the latest definitions and features. This helps in identifying newly discovered vulnerabilities and ensures that the scanning process remains effective against emerging threats.
- Training and Awareness: Ensuring that staff members are trained on the importance of vulnerability scanning and how to interpret its results is vital. Enhanced awareness can lead to better compliance with security protocols and more effective remediation efforts.
- Document and Track Findings: Keeping detailed records of scan results, vulnerabilities found, and remediation actions taken is important for accountability and continuous improvement. Documentation can help in tracking trends over time and assessing the overall effectiveness of the vulnerability management process.
What Common Vulnerabilities Can Be Detected by Vulnerability Scanners?
Common vulnerabilities detected by vulnerability scanners include:
- Missing Patches: Scanners identify systems that are not updated with the latest security patches, which can leave them exposed to known exploits.
- Weak Passwords: These tools can evaluate password strength and detect accounts that use easily guessable or default passwords, increasing the risk of unauthorized access.
- Open Ports and Services: Vulnerability scanners check for open network ports and running services that may be unnecessary or insecure, potentially enabling attackers to gain entry.
- Misconfigured Security Settings: They assess system configurations for security best practices, identifying settings that may inadvertently expose systems to threats.
- Outdated Software: Scanners flag outdated software versions that may have known vulnerabilities, prompting updates to mitigate security risks.
- Unsecured Applications: Scanners can detect web applications or APIs that lack proper security measures such as input validation, making them susceptible to attacks like SQL injection.
- Insecure Network Protocols: They identify the use of outdated or insecure protocols, such as FTP or Telnet, which can lead to data interception during transmission.
- Compliance Violations: Vulnerability scanners help organizations identify areas where they do not meet regulatory compliance standards, ensuring adherence to laws and regulations.
What Best Practices Should Organizations Follow When Using Vulnerability Scanners?
Organizations should adhere to several best practices when using vulnerability scanners to enhance their cybersecurity posture.
- Regular Scanning: Conduct vulnerability scans on a regular basis to identify new vulnerabilities that may arise over time. This practice helps in maintaining an up-to-date security stance, as new vulnerabilities are discovered frequently and can be exploited if left unchecked.
- Comprehensive Coverage: Ensure that the scanning encompasses all assets within the organization, including servers, workstations, and mobile devices. By scanning all components of the network, organizations can identify vulnerabilities that may exist in less obvious areas, thus reducing the potential attack surface.
- Prioritize Vulnerabilities: Use a risk-based approach to prioritize vulnerabilities based on their severity and the potential impact on the organization. By addressing the most critical vulnerabilities first, organizations can effectively mitigate risks and allocate resources where they are needed most.
- Integrate with Other Security Tools: Integrate vulnerability scanners with other security tools such as intrusion detection systems and patch management solutions. This integration enables a more holistic view of the security landscape and ensures that vulnerabilities are not only identified but also remediated in a timely manner.
- Customize Scanning Settings: Tailor the scanning settings to fit the specific environment and requirements of the organization. Customizing settings allows for more relevant results, reduces false positives, and improves the overall effectiveness of the scans.
- Regularly Update Scanning Tools: Keep the vulnerability scanning tools and their databases up to date to ensure that the latest vulnerabilities are detected. Regular updates help in maintaining the effectiveness of the scanning process and adapting to the evolving threat landscape.
- Document and Track Findings: Maintain detailed records of scan results, including findings, remediation actions taken, and follow-up scans. This documentation is crucial for compliance, audits, and understanding the organization’s vulnerability management progress over time.
- Training and Awareness: Provide training for staff on the importance of vulnerability management and how to interpret scan results. Educating employees fosters a security-focused culture and helps ensure that vulnerabilities are addressed effectively across the organization.
- Plan for Remediation: Develop a clear plan for addressing vulnerabilities, including timelines and responsibilities for remediation efforts. An organized approach to remediation ensures that vulnerabilities are resolved efficiently and helps to minimize potential risks.
How Often Should Vulnerability Scanning Be Conducted for Maximum Effectiveness?
For maximum effectiveness, vulnerability scanning should be conducted regularly and strategically.
- Regular Schedule: Conduct scans at least quarterly to ensure that new vulnerabilities are identified and addressed promptly.
- After Significant Changes: Perform scans immediately after any major system updates, installations, or changes to the network infrastructure.
- Compliance Requirements: Adhere to any industry-specific regulations that mandate a specific frequency for vulnerability assessments.
- Continuous Scanning: Implement automated, continuous scanning solutions to monitor for vulnerabilities in real-time and respond quickly to new threats.
- Risk Assessment Based: Adjust scanning frequency based on the risk profile of the assets, with higher-value or more sensitive systems requiring more frequent scans.
Regular scheduling of vulnerability scans ensures that organizations can keep up with the evolving threat landscape and address vulnerabilities before they can be exploited. Quarterly scans provide a baseline, allowing teams to track improvements and identify recurring issues.
After significant changes, such as software updates or changes in network configuration, conducting scans is crucial because these modifications can introduce new vulnerabilities. This practice helps to maintain the security of the system during transitional phases.
Compliance requirements often dictate the frequency of vulnerability scans, especially in regulated industries like finance or healthcare. Ensuring compliance not only protects the organization but also minimizes legal and financial risks.
Continuous scanning helps organizations maintain a proactive security posture by providing ongoing visibility into potential vulnerabilities. This approach allows for immediate responses to newly discovered vulnerabilities, significantly reducing the window of exposure.
Finally, tailoring scanning frequency to the risk assessment of specific assets ensures that critical systems receive the attention they need. Higher-risk assets may require more frequent scans to safeguard sensitive data and maintain regulatory compliance.
What Future Trends in Vulnerability Scanning Technologies Should Organizations Be Aware Of?
Future trends in vulnerability scanning technologies organizations should be aware of include:
- AI and Machine Learning Integration: The incorporation of AI and machine learning will enhance the accuracy and efficiency of vulnerability scanning. These technologies can analyze vast datasets to identify patterns and predict potential vulnerabilities, allowing for more proactive security measures.
- Automation and Continuous Scanning: Organizations are moving towards automated vulnerability scanning solutions that provide continuous monitoring. This approach helps in identifying vulnerabilities in real-time, reducing the window of exposure and enabling quick remediation actions.
- Integration with DevSecOps: Vulnerability scanning tools are increasingly being integrated into the DevSecOps pipeline. This allows for early detection of vulnerabilities during the development phase, fostering a culture of security-first in software development.
- Cloud-Based Vulnerability Management: As organizations shift to cloud environments, cloud-based vulnerability scanning solutions are becoming more prevalent. These tools are designed to scan cloud configurations and services, ensuring that organizations maintain compliance and security in dynamic cloud environments.
- Focus on IoT and Mobile Device Security: With the growing number of IoT devices and mobile applications, vulnerability scanners are evolving to address the unique security challenges these technologies present. This includes scanning for vulnerabilities in the firmware and ensuring secure communication between devices.
- Enhanced Reporting and Visualization: Future vulnerability scanners will offer improved reporting and visualization features, providing organizations with better insights into their security postures. This will enable security teams to prioritize vulnerabilities based on business impact and streamline remediation efforts.